DPDP Compliance Guardrails for Claude
If your teams already use Claude, India's Digital Personal Data Protection (DPDP) Act makes your organisation responsible for the customer data they share with it, including the files Claude Desktop, Cowork and plugins open on their own. This post explains which guardrails you need around that usage, and how the Mavs secure gateway puts them in place without changing how your teams work.
By Manjul Kubde, Co-founder & Abeer Sehrawat • Sep 29, 2026
Can you use Claude and stay DPDP compliant?
Yes, with the right guardrails around it. The DPDP Act doesn't ban AI tools, but it makes your organisation responsible for the personal data your employees share with Claude. When your organisation decides how customer data is used, it is the Data Fiduciary, and it stays accountable for that data even after Anthropic receives it (Section 8(1)).
If that data leaks from Anthropic's systems, the breach is still yours to report to the Data Protection Board and to every affected customer (Section 8(6)), and the fine for not having reasonable security safeguards goes up to ₹250 crore (Section 8(5)). These obligations apply from 13 May 2027, and data shared with Claude today may still be held then.
So if your teams are already using Claude, these guardrails need to be in place around that usage now:
- Personal data protected before it reaches Anthropic.
- A policy for how each team uses Claude.
- A record of every interaction.
Why Claude Desktop, Cowork and plugins are harder to govern
Claude chat carries the same risk as any chat window. With Claude Desktop, Cowork and plugins, the exposure goes beyond what someone types.
- One request can read a whole folder. Cowork opens and edits files on the employee's machine, so a client spreadsheet can go to the model as part of a single task.
- Connectors pull data in. Claude can pull customer records from connected email, drives and CRM (customer relationship management) systems into a task without human review.
- Office and Outlook plugins reach into other apps. Claude's plugins for Excel, PowerPoint and other Office apps, and for Outlook, work on the open spreadsheet, deck or email, so its customer data goes to the model too.
- Personal accounts can keep chats for years. On Claude's Free, Pro and Max plans, users choose whether Anthropic can use their chats for training. If they allow it, Anthropic keeps the data for five years, and 30 days otherwise (Anthropic).
Long retention clashes with your customers' rights as Data Principals. If a customer withdraws consent or asks you to erase their data, you have to make sure it is erased, including by anyone processing it for you (Sections 8(7) and 12). Anthropic's own guidance for Cowork advises against giving it access to files with sensitive information, which is where most real work sits.
For more on the security safeguards the DPDP Rules expect, read what DPDP Rule 6 requires when you use AI.
How to make Claude usage DPDP compliant with the Mavs secure gateway
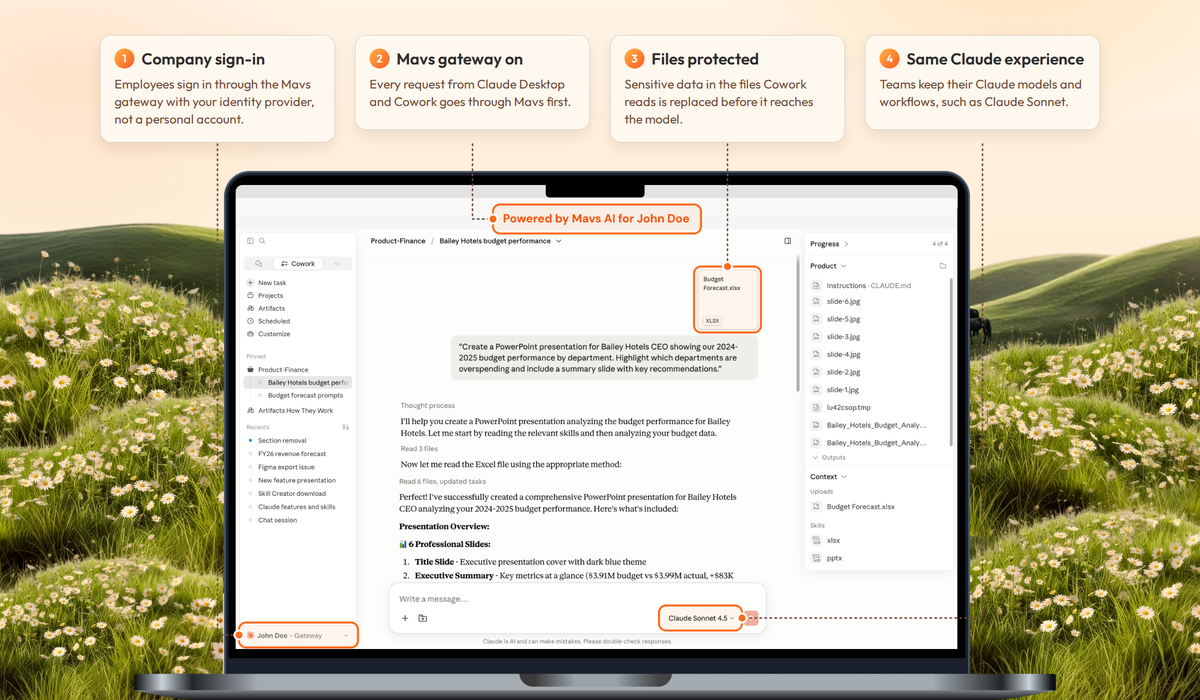
Claude Desktop secured by Mavs is the standard Claude Desktop app with Mavs in front of it as a runtime gateway. It governs Claude Desktop rather than replacing it, so your teams keep working in it using the same tasks, files, projects and skills. Every request goes through Mavs before it reaches the Anthropic model you configure, such as Claude Opus 5.5 or Claude Sonnet 5, which ensures your usage is DPDP compliant.
- Prompts and files protected. Sensitive values in prompts and in the files Claude works on are replaced with synthetic stand-ins instead of being blocked, then restored on the way back, so the whole security process is invisible to the employee while work continues unobstructed.
- AI policy. Configure policy for Claude usage based on the kind of data being processed, enforced at runtime on every request.
- Office and Outlook plugins covered. Claude's plugins for Microsoft Office apps and Outlook go through the same gateway, so employees can work deeply in their spreadsheets, decks and emails while the sensitive data is not shared with the models.
- Sessions you can reconstruct. Prompts, tool calls and policy actions are recorded in tamper-evident logs, so you can see what an agent did in any session and prove your compliance.
- Connectors decided centrally. An admin decides which connectors each team can use.
- Risk and productivity dashboard. See top risks, actions taken, prompts processed and adoption by team.
- Sign-in through your identity provider. IT pushes the app through MDM, and employees sign in with your identity provider, such as Microsoft Entra ID, so access follows your existing groups and offboarding.
- Data residency. The real sensitive values stay with your organisation, and only stand-ins reach Anthropic. Wherever Claude processes a prompt or stores history, your customers' personal data isn't there.
- Cost follows usage, not headcount. Tokens are billed against your Anthropic API licence rather than per seat, and you can set token limits.
Read how a SEBI registered investment advisory firm uses Claude secured by Mavs to analyse client portfolios.
What data does Mavs replace before it reaches Claude?
Mavs covers common Indian personal data in prompts and files, as well as confidential business information.
| Category | Examples |
|---|---|
| Government IDs | PAN, Aadhaar, voter ID, passport, driving licence |
| Financial data | Bank account and card numbers, UPI IDs, demat account numbers, loan and insurance policy numbers |
| Personal details | Names, addresses, phone numbers, email addresses |
| Health | Patient IDs, medical record numbers, health insurance claim numbers |
| Business information | Deal and project codenames, unannounced pricing, merger and acquisition terms, key accounts, unreleased roadmaps |
Business sensitive information isn't personal data, so the DPDP Act doesn't cover it. But sending it to a third-party model is a risk in itself, and some of it is regulated elsewhere, such as price-sensitive information under the Securities and Exchange Board of India (SEBI) insider trading rules, or client data covered by a non-disclosure agreement (NDA). Mavs Secure Chat also lets you secure your business sensitive data in addition to PII.
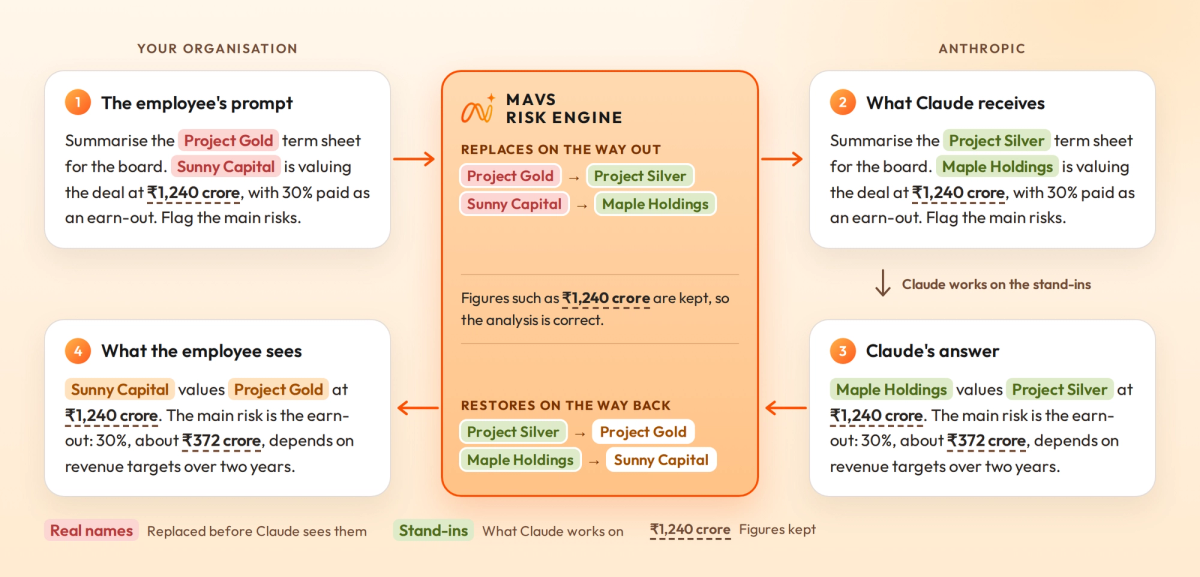
For example, an employee asks Claude to summarise a deal term sheet for the board. The Mavs risk engine replaces the deal and investor names before the prompt reaches Anthropic and keeps the figures as they are, so Claude's analysis is still correct. The employee then sees the answer with the real names restored.
Frequently asked questions
Is Claude DPDP compliant?
Under the DPDP Act, your organisation is responsible for the personal data it collects, whichever AI tool it uses. If your teams use Claude with customer data, put guardrails in front of it that protect the data before it reaches Anthropic, and keep a log of every interaction as evidence of your compliance.
Does Claude train on the data employees share with it?
On Claude's Free, Pro and Max plans, it can if the user allows it, and Anthropic then keeps the data for five years. With the Mavs secure gateway, the sensitive data is replaced before it reaches Anthropic, so your real customer and business data is never shared with Anthropic for it to train on.
Can employees use Claude Cowork with customer files and stay DPDP compliant?
Yes, if the sensitive data in those files is protected before it leaves your organisation. Anthropic's own guidance advises against giving Cowork access to files with sensitive information. But with the Mavs secure gateway, you can use Claude with sensitive files because Mavs replaces the sensitive data in the files Cowork opens, from personal details and government IDs to financial, health and confidential business information, with realistic stand-in values, and keeps the figures the analysis needs, so the work can go ahead on the full file.
How can organisations add guardrails to Claude for personal data?
Run Claude Desktop through the Mavs secure gateway, which applies guardrails you set for each team before anything reaches Anthropic. It replaces personal data in prompts and files, enforces your policy and logs every action.
How can organisations get an audit trail of Claude usage for DPDP compliance?
Run Claude Desktop through the Mavs secure gateway. Mavs audit logs record every prompt, tool call, replacement and policy decision in a tamper-evident record, so you can show an auditor how personal data was handled in any session. Rule 6 of the DPDP Rules asks you to keep logs that help detect and investigate unauthorised access to personal data, and to retain them for one year.
Do employees have to change how they use Claude?
Not if the guardrails sit in front of Claude rather than replacing it. With the Mavs secure gateway, employees keep working in Claude and the Office and Outlook plugins, as they do today. IT rolls it out through mobile device management (MDM), employees sign in with your identity provider, and sensitive data is replaced and restored in the background without any friction for employees.